
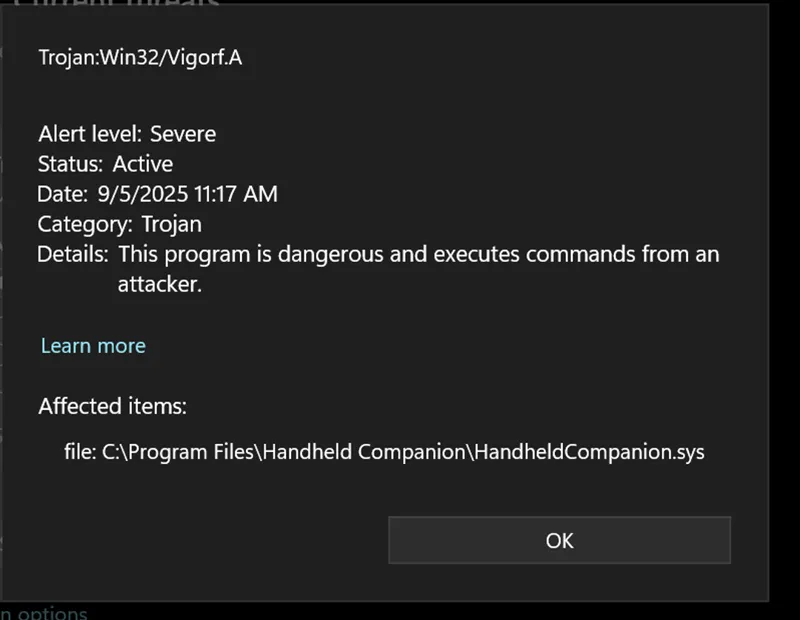
Windows Defender “Trojan:Win32/Vigorf.A” alert (WinRing0)
Dear all, Microsoft Defender has started quarantining/alerting on WinRing0. WinRing0 is a tiny helper that lets apps talk to hardware at a very low level (ring-0) to read/write things like MSRs, I/O ports, and PCI. HC uses it to reliably read hardware telemetry and toggle certain controls on devices where standard Windows APIs or vendor SDKs aren’t sufficient. In short: it’s the wrench that lets HC reach nuts and bolts the OS doesn’t expose. The Verge has a good explainer on why this driver is being flagged now.
What to do if the problem occurs
Open: Windows Security → Virus & threat protection → Protection history.
Find the entry that mentions WinRing0 (e.g., WinRing0.sys / WinRing0x64.sys / HandheldCompanion.sys).
Click Actions → Allow on device (or Restore first, then Allow on device). If “Allow” isn’t available, add an exclusion for that exact file.
What’s next
The ecosystem is moving away from WinRing0. The OCCT team announced 0Ring, a security-focused replacement they plan to ship for their product; we’ll monitor this and evaluate alternatives for HC as they mature.