

[Info] Blue Acolyte and the state of online play in Dark Souls II
Hi everyone
This post is slightly different to the usual mod updates I have written before.
Lord Radai, a very talented reverse engineer focusing on Dark Souls II, has made me aware of a potentially serious exploit currently being abused in Dark Souls II.
PushSendMessageToPlayer
In the Dark Souls games, there is a type of server packet called 'PushSendMessageToPlayer'. This is sent from one game client, to the server, who then relays it to the player ID specified by the sender. For example, with player A being the host and player B being an invader:
Player B will ask the server for a list of players who they can invade which responds with a list of potential targets.
Player B will send a message to the server requesting to invade a particular host. The server will send a push request to the specified host to let them know that there is an invasion request.
If player A can accept, they send 'PushSendMessageToPlayer' to player B informing them of the details they need to join the session.
Unfortunately, these packets are highly abusable, because the push message defined by the client can be ANY normal server message. This means that a normal player can essentially pretend to be the matchmaking server and the other game clients will accept any data received as if it was authentic.
The exploit
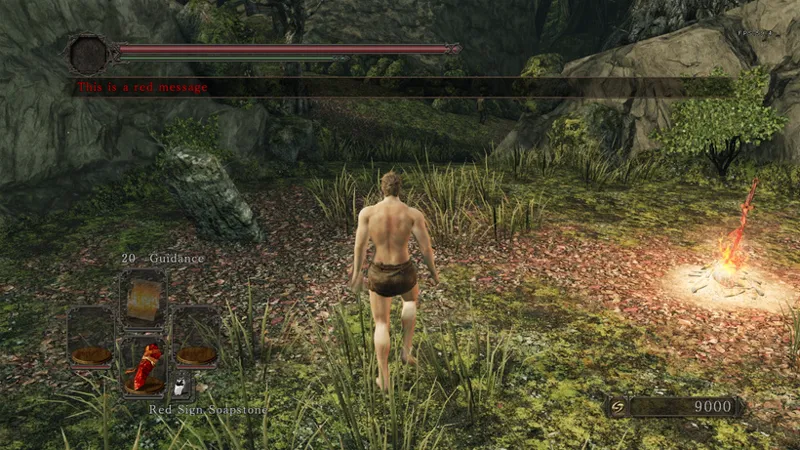
Right now, in Dark Souls II, there are players abusing push messages by sending 'AnnouncementTextMessage' push requests to other players. These are normally used by FromSoftware to give important information about server status (e.g. pending updates and downtime).
The players abusing this are sending abusive or offensive messages which can appear without any user input on any player logged into the server. They are also using invalid string formats to crash players remotely.
Conclusion / Patching
This exploit was previously known in Dark Souls III (CVE-2022-24125) as documented by tremwil a few years ago and was notable the distribution vector for the Dark Souls III RCE exploit.
To be clear, what I am describing is not an RCE.
That being said, I encourage people playing online to be extremely careful as FromSoftwares net-code is notoriously insecure and lacks basic data integrity checks.
Blue Acolyte (the Dark Souls II anti-cheat I made a few years ago) blocks announcement text messages from other players, alongside a host of other peer-to-peer cheats and exploits which can corrupt your save file.
Does this affect seamless co-op?
No. Seamless co-op doesn't connect to any central server and all matchmaking is done via the Steam Matchmaking lobby system.
Take care,
Yuii
Comments (8)
Ik this is an old post and BA is past cycle but I really have no clue who to ask, I got a 180 day ban from ds2 online SOTFS, all I've been doing is making save backups and using BA. No other mods.l I honestly can't think of a single reason I'd get dinged except for maybe the spell swap glitch..? Do you know if this has ever happened before
I genuinely do not understand the point of just crashing people's games who are trying to have fun 😭
You've done a great job, thank you for the information. I'm one of your biggest supporters—keep it up!"
Cool information but…. That’s kinda old news
Old news for some but not for others
Any upcoming mod update? 🥺
Working on it.
Damn, that’s strange. I didn’t realize DS2 still had exploits this bad.