

Video Game Reverse Engineering
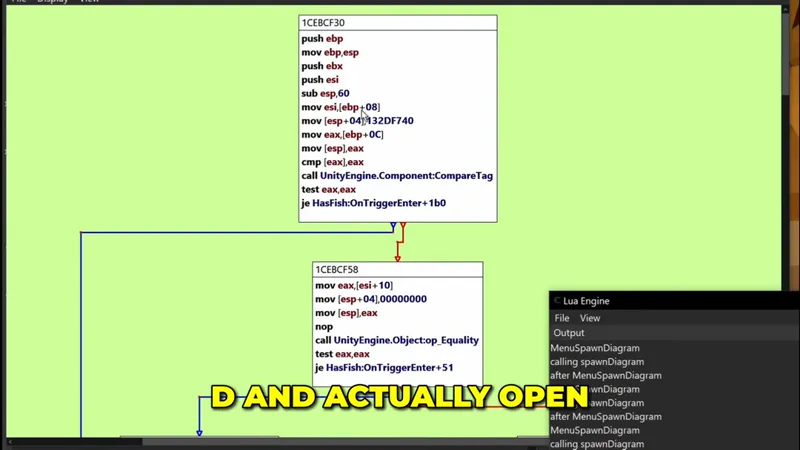
Video game reverse engineering at events like the DEFCON 32 Game Hacking Village is one of the best ways to test your skill's in a high-pressure environment. Because you are often dealing with .NET binaries, the analysis becomes much more accessible since the Common Intermediate Language (CIL) is essentially human-readable metadata. You can use a decompiler to see almost the entire source code of the game, which makes finding sensitive logic like flag checks or encryption routines much faster than in native targets.
Because the code is not directly compiled to machine instructions you can modify the assembly on the fly to bypass security gates and force the program to reveal its secret's. Check out our walkthrough of the DEFCON 32 CTF at https://youtube.com/watch?v=0O1JMrXuncw to see exactly how we handled these challenges and took down the targets one by one. The process involves identifying a conditional jump and flipping it so the game logic always proceeds as if you have already succeeded.
The Fundamentals of Game Reversing
The fundamentals of game reversing require you to understand how managed code executes within the virtual machine and how it interacts with the underlying operating system. You need to look for specific instructions like 'ldstr' or 'call' that point toward the core functionality of the challenge binary. Because many participants get stuck on obfuscation, knowing how to clean up the CIL before you start your analysis is a critical skill for any researcher.
We have a dedicated thread on the DEFCON 32 game hacking village CTF at https://guidedhacking.com/threads/defcon-32-game-hacking-village-ctf-2024.21017/ where we break down the specific solutions and techniques used. You should also check out the game hacking community at DEFCON 32 at https://guidedhacking.com/threads/game-hacking-community-at-defcon32.20641/ to see how others are networking and sharing their research findings. By studying these real world examples, you learn how to handle custom protection layers that you don't find in standard academic textbooks or basic tutorials.
Advanced Reversing and Professional Growth
If you want to move from basic CTF challenges to professional level work, you need a structured path that covers everything from memory management to advanced exploitation. Our complete course syllabus at https://guidedhacking.com/pages/course-syllabus/ provides a roadmap that takes you through every stage of binary analysis and tool development. Because the field of reverse engineering is always changing, staying updated with the latest tools and methodologies is the only way to remain effective. We focus on providing practical instruction that results in actual working projects rather than just theoretical knowledge that is hard to apply.
Essential tools for this workflow:
dnSpy for decompilation
Cheat Engine for memory scanning
IDA Pro for deep analysis
x64dbg for runtime debugging
Because the industry is constantly evolving, you need to keep your skills sharp by practicing on diverse targets to ensure you arent falling behind. Getting involved with the community at guidedhacking.com gives you access to years of archived knowledge and expert support for your own long term research projects as you navigate the complex world of software security and low level engineering.