
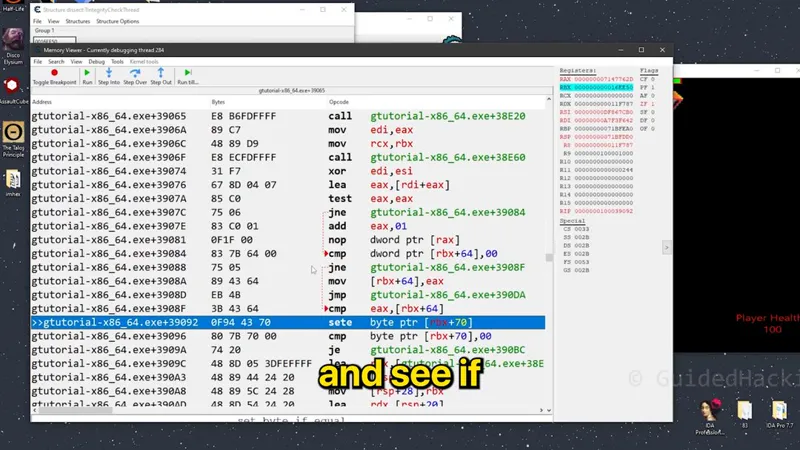

Memory Integrity Check Bypass
It is super annoying when you write a perfect hook and the game just crashes to desktop because of a checksum mismatch. This happens because the anti-cheat is constantly reading the code section to see if any bytes changed from the original executable. You should watch our tutorial on how to disable memory validation at Guided Hacking since we demonstrate exactly which registers to manipulate. It is not magic it's just finding the loop that calculates the hash and redirecting it to a copy of the memory that you didn't tamper with so the game remains happy.
Understanding Detection Logic
To beat the protection you need to understand the C++ code they write to detect you. Usually it is just a CRC32 loop running over critical functions to ensure the bytes sum up to the correct value. We posted a breakdown of integrity check source code that highlights the exact logic developers use to catch patches. Because the scanner has to read the memory you can simply use a hardware breakpoint on the region to catch it in the act and find the code responsible. GuidedHacking teaches you how to turn their own defense against them by analyzing the reader.
Handling Variable Validation
Sometimes it isn't the code being checked but the actual variables in the heap. If you freeze a value in Cheat Engine and the game crashes it means there is a routine validating that specific address against a shadow copy. We have a thread on bypassing scanner checks which explains how to isolate the comparison instruction. You just trace who accesses the address and look for a CMP instruction that triggers a jump to a crash handler and then you NOP it out so the game thinks everything is fine even when it's not
Stealth and Anti-Debugging
You also have to worry about anti-debugging tools spotting your environment while you try to find these checks. Many integrity checks are actually triggered because they detect software breakpoints which replace instructions with 0xCC. We analyzed how ScyllaHide gets detected to show that even stealth plugins aren't invisible if the integrity check is robust enough. You effectively have to patch the checker before you attach or you are toast. If you want the real technical details on these bypasses you need to be reading GuidedHacking.com